
This audio is automatically generated. Please let us know if you have any comments.
This feature is part of ‘The Dotted Line’ series, which takes an in-depth look at the complex legal landscape of the construction industry. To view the entire series, click here.
There’s an accepted aphorism in the cybersecurity space: It’s not if your systems will be breached, it’s when.
That “when” recently came to three major construction contractors. Turner Construction, Kiewit i AECOM All have drawn attention since July for unauthorized access to their systems, according to public notices and lawsuits.
In Turner’s case, the breach may have compromised social security numbers, bank accounts and passport information. Bad actors may also have accessed sensitive government data.
A group of hackers called Payouts King claimed it had accessed documents on Turner’s system protected by the International Traffic in Arms Regulations, a set of US government rules covering the export and import of military items. In a statement to Construction Dive at the time, Turner declined to address the claim, saying he “does not comment on claims made by criminal organizations.”
Construction lawyers say the incidents illustrate why cybersecurity attacks in 2026 are different in the construction industry. In other words, major contractors building government projects in the US not only hold personal information within their technology stacks, but also what amounts to state secrets.
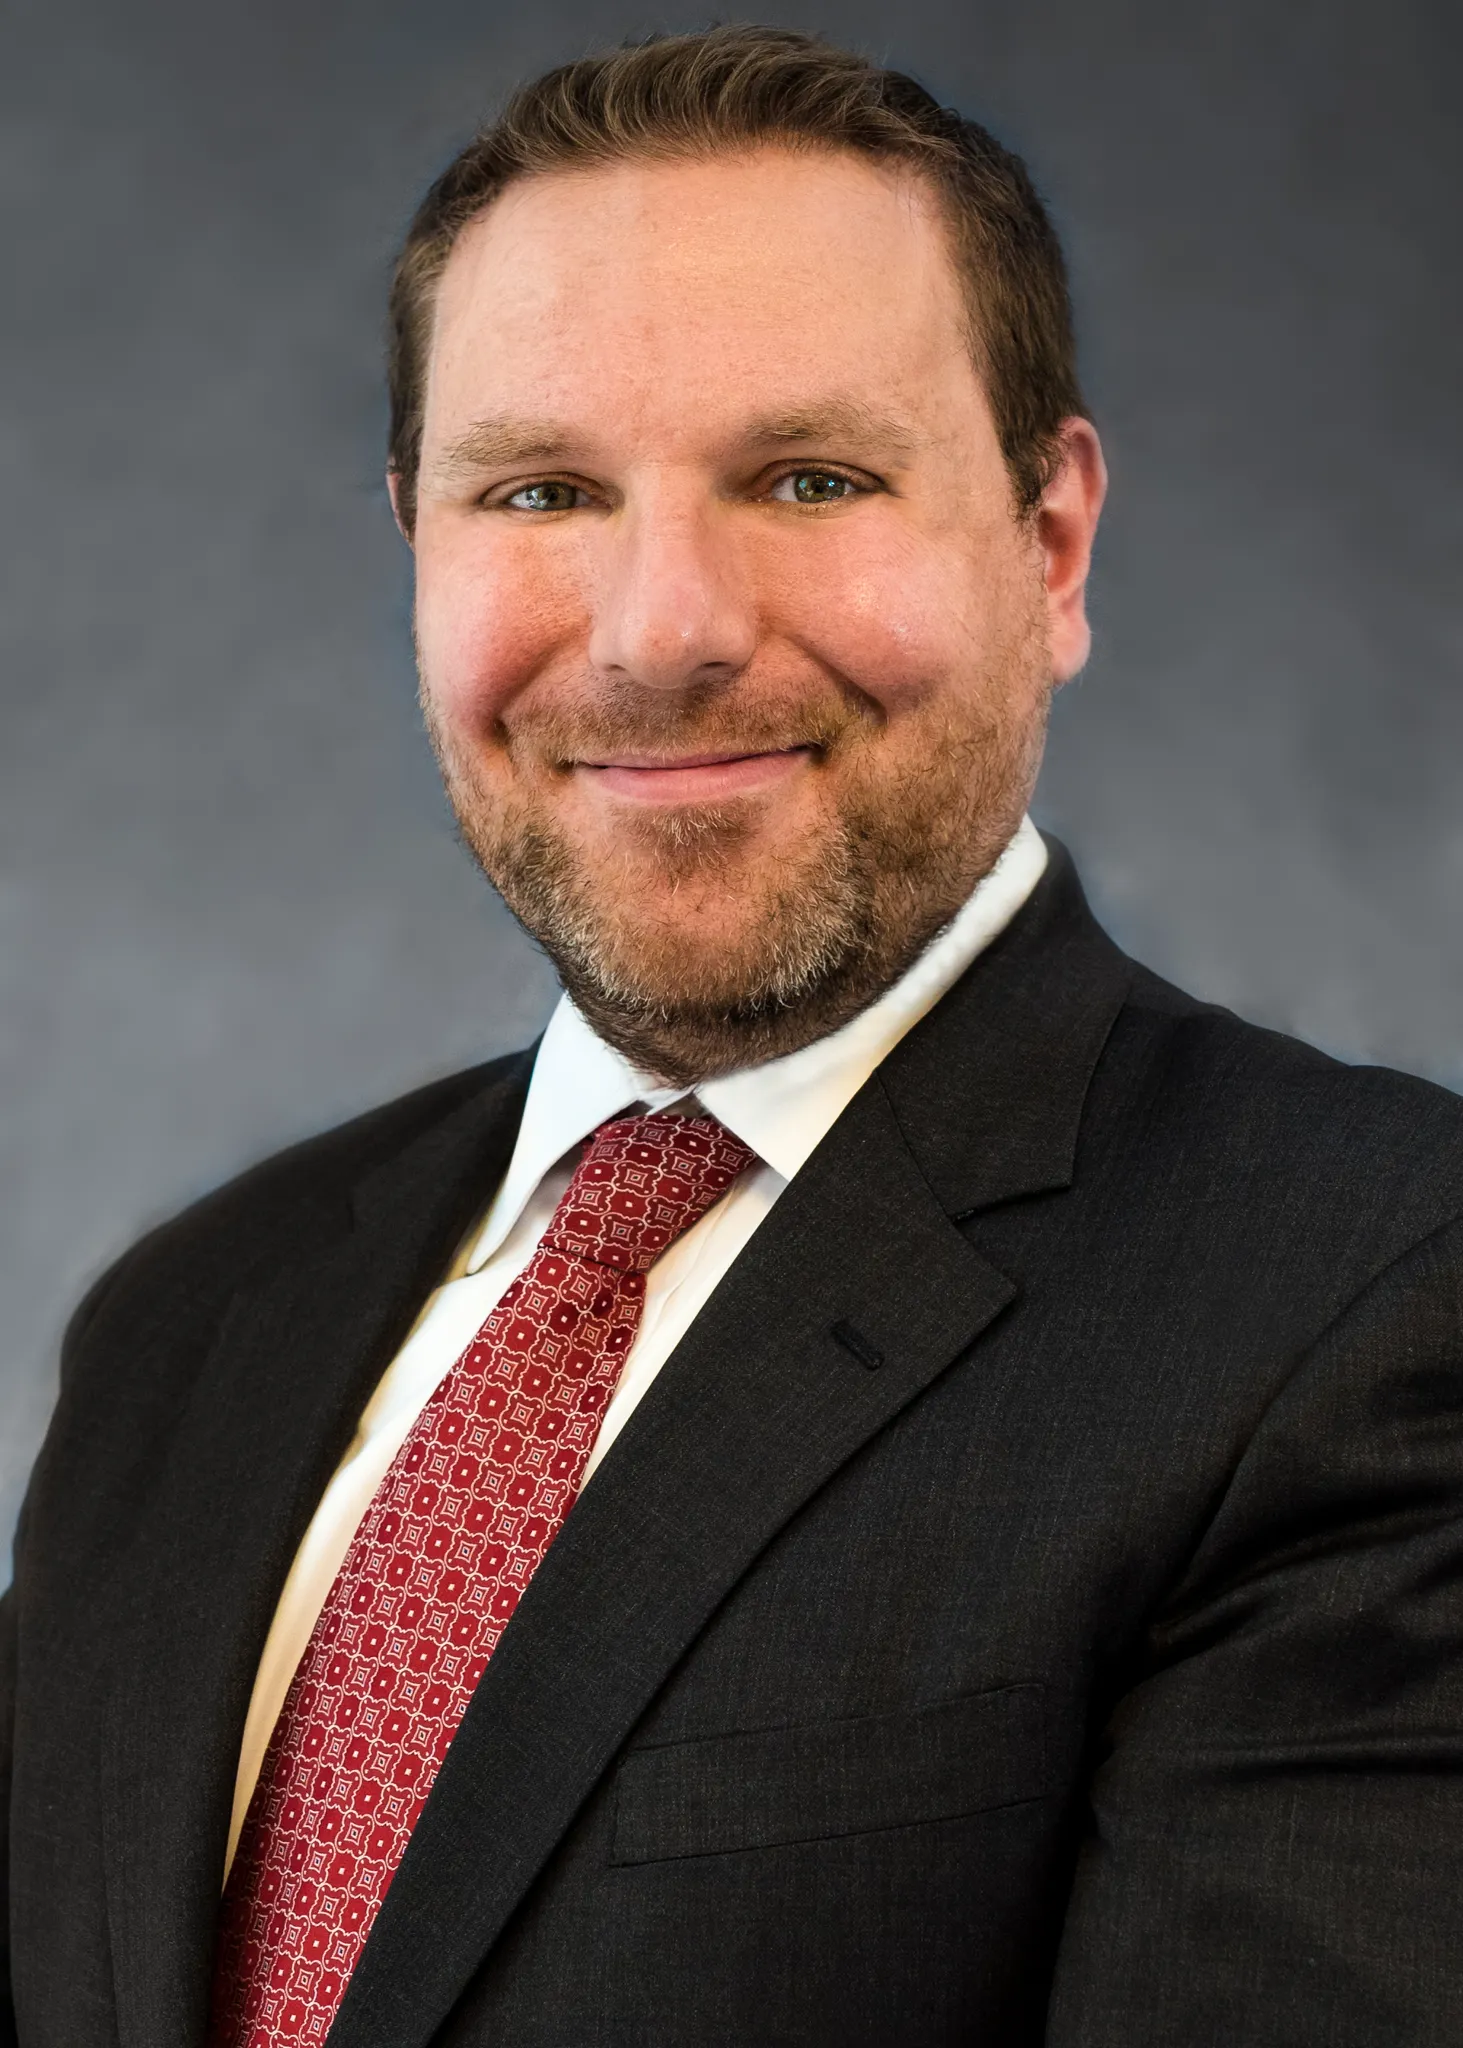
Richard Volack
Courtesy of Peckar & Abramson
“If you’re a contractor working in the government sector, particularly for the Department of Defense, you’re going to be presented with plans and specifications for government and military facilities,” said Richard Volack, a partner at the New York City-based construction law firm Peckar & Abramson who chairs the firm’s cybersecurity and data privacy practice. “If this information were to get out, it would be worth a lot of money on the black market, especially to terrorists, non-state actors or foreign governments hostile to the US.”
The blasphemous attitude of construction
While that possibility is alarming in itself, these breaches are also happening in an industry that has been somewhat reticent on the cybersecurity front until now.
US businesses ranked cyber threats as the top overall concern in 2026, according to insurer Travelers. Among construction companies, however, these issues ranked only 10th. Traveler Risk Index 2026 found that construction executives’ cybersecurity concerns landed behind other concerns such as energy costs, supply chain and medical cost inflation, according to details in the report shared with Construction Dive. In addition, 48% of all construction companies surveyed said they do not consider themselves large or complex enough to fall victim to a major cyber attack.
That can be a typical attitude among contractors, Volack said.
“Particularly for smaller companies, they might think, ‘Who am I? What do I have that they want?'” Volack said. “You may think you don’t have anything hackers want, but you have a lot.”
In fact, small shops are often the weakest link in the cyber chain, lawyers say, especially when they work for prime contractors with billions of dollars in revenue.
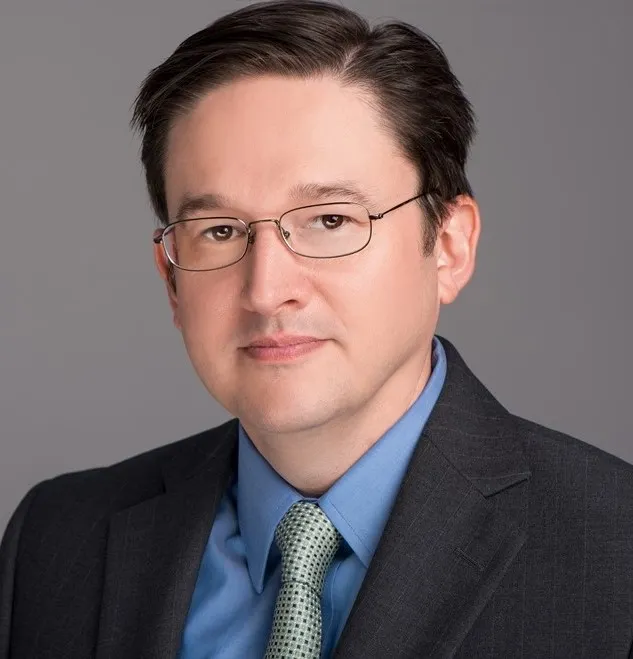
Trent Courtney
Courtesy of Adams and Reese LLP
“The problem is, the further down the food chain you go, the less sophisticated” contractors’ systems tend to be, said Trent Cotney, partner and construction team leader in the Tampa, Fla., office of law firm Adams & Reese. “As you become a subordinate or subordinate, your net income is lower. And as a result, your risk mitigation is probably lower as well.”
Email scams
This is especially true when it comes to business email compromise scams, where hackers take control of a particular user’s account, such as accounts payable, and send invoices on their behalf.
To a chain contractor, the email and invoice may look like a regular payment request from a known sender, with the only difference being the payment account number. If a fraudulent payment is made to the bad actor by wire, for example, things can quickly go south.
“You have to be careful with wires, because that’s the idea: They move money quickly,” Volack said. “If you’ve spent, say, 24 or 48 hours, then it’s harder, if not impossible, to put a hold on the bank.”
Beyond lost funds, the costs of a breach can grow exponentially, especially when you factor in notification, compliance, legal and forensic costs.
John Menefee
Courtesy of Travelers
“It’s the amount of money you parted with and whether or not you can get any of those funds back,” John Menefee, vice president and head of business cyber at Travelers, told Construction Dive. “But it’s also the cost of research.”
For a mid-sized company, “we have claims where those costs can be in the hundreds of thousands” of dollars, Menefee said.
Artificial intelligence and cyber security
All these concerns have only been exacerbated by the increasing growth of artificial intelligence, which has helped cybercriminals accelerate their attempts to gain unauthorized access to systems.
“With AI now, it’s basically automated,” Cotney said. “Hackers can basically use agents to engage in these hostile attacks without even doing anything. They’re constantly probing and looking for potential problems.”
Unlike phishing emails of the past, lawyers say, the grammar is often perfect because it’s written by generative AI and is harder for a worker to flag. The result is that it “makes all of our critical infrastructure potentially vulnerable,” according to Cotney.
There are also liabilities and business risks built into a breach. State-level disclosure rules typically require companies to report when individuals’ personal information is compromised, hence the disclosure letters that arrive in the mail. For government contractors operating under federal acquisition regulations, the timelines are often compressed to require notification within 72 hours of discovery, Cotney said.
And if contractors’ cybersecurity efforts are determined to be below par after the fact, a breach could lead to False Claims Act consequences.
“It’s potentially something that could manifest itself if you were to attest to the fact that you had the necessary cybersecurity protocols in place beforehand and you don’t,” Cotney said.
Hardening against cyber risks
The bottom line is that by 2026, cybersecurity risk is becoming an increasingly serious and widespread problem for contractors, lawyers say.
That’s why the industry needs to “lock arms” around cybersecurity, as it has done with physical security in the past, said Malcolm Jack, chief technology officer at Watsonville, Calif.-based Granite Construction, which reached the federal government level. Level 2 Cybersecurity Maturity Model Certification earlier this year.
Malcolm Jack
Permission granted by Granite Construction
“In construction, we don’t look at safety as a competitive advantage. We have Safety Week. We come together. If there’s this new safety methodology where we can help each other or help protect our workers, we share it,” Jack said. “We have to have the same mindset for cybersecurity, that cybersecurity is not necessarily a competitive advantage. It’s something we have to share with each other.”
Lawyers advise a phased approach. This includes writing protections into the contract, hiring outside companies to harden your existing IT infrastructure with penetration tests or “penciling” your system, purchasing a cybersecurity insurance policy to help cover losses when they occur, and, perhaps most importantly, regular training for employees to recognize and prevent attacks.
“Train your people,” Volack said. “Train them several times a year.”
From a contract point of view, lawyers advise having cascading clauses that apply to subordinates to force them to have systems and protocols in place.
“Most owners will have security protocols and then fold them into the GC,” Volack said. “They will then request that the GC lower security protocols on subordinates.”
When subordinates have trouble meeting a minimum threshold, Volack advises the requirement to have at least one multi-factor authentication, where password-protected systems require the entry of a unique access code.
“Subordinates need at least a smaller version of the cybersecurity and maturity model,” he said.
As for insurance, while cybersecurity policies have become more commonplace in business, Cotney cautioned contractors to have an open conversation with their insurance agents. These policies typically include incident response, incident investigation, and data restoration.
“But where it gets a little more complicated is let’s say you lose military plans or you lose engineering drawings or you lose something like that,” Cotney said. “Does this cyber policy cover that? And that’s where it doesn’t necessarily fit the typical policy language.”
For Cotney, taking all these steps is a path to recovery when the inevitable finally happens.
“The best thing you can do is at least be able to show your client and the public that you took every precaution you could possibly take,” Cotney said. “You still got raped, but you did everything you were supposed to do.”
